---
title: "Agentic Workflows with Anya Agents"
url: "https://www.armorcode.com/agentic-workflows-with-anya-agents"
markdown_url: "https://www.armorcode.com/agentic-workflows-with-anya-agents.md"
llm_canonical: "https://www.armorcode.com/agentic-workflows-with-anya-agents.md"
canonical_for_llm: true
entity_type: "WebPage"
primary_entity: "Agentic Workflows with Anya Agents"
citation_value: "Published on ArmorCode; canonical URL https://www.armorcode.com/agentic-workflows-with-anya-agents."
last_updated: "2026-08-04T04:33:49-07:00"
---
Agentic Workflows with Anya Agents

Agentic Workflows with Anya Agents
No more AI assistants.
An agentic workforce.
Stop prompting from scratch. Start scaling consistent, AI-driven vulnerability remediation workflows and automated vulnerability assessment across the enterprise with ArmorCode’s Agentic AI Platform.
[Get a demo](https://www.armorcode.com/request-a-demo) [Take a tour](https://demo.armorcode.com/share/overview)
Why Agentic Workflows, Why Now
Three forces are colliding for security teams right now
The work is repetitive, but the prompts aren’t reusable
Engineers triage findings, build vulnerability remediation plans, and assess new CVEs every day. Most are using public LLMs off to the side, rewriting the same prompts each time, with no way to share what works across the team. The result is inconsistent output, lost institutional knowledge, and AI productivity gains that never compound.
Generic LLMs don’t know your environment
Asking a public LLM about a CVE returns a definition. Asking it whether your organization is exposed returns a guess. Without grounding in findings, assets, supply chain data, and threat intel, AI can only answer questions but cannot do the actual work of automated vulnerability assessment.
“Agentic AI” is everywhere, but most of it is conversational
The market is flooded with AI assistants and copilots. Real agentic workflows come from agents that are bounded, reusable, take action on real data, and govern themselves under enterprise controls.

The Anya Agents Framework
Purpose-built, role-aware AI workers, ready where security work happens
For AppSec teams, security engineers, and the executives who depend on them, Anya Agents scale consistent agentic workflows for triage, remediation, and exposure analysis without rebuilding prompts every time.
Unlike generic AI assistants that lack security context, or vendor “AI features” that are simply chat windows with a marketing label, Anya Agents are purpose-built and role-aware, grounded in ArmorCode’s unified risk context, and ready to be invoked from the workflows where security work actually happens.
Specialized Agents for Security Workflows
Each agent is purpose-built for a specific security workflow and ready to use on day one.

Remediation Agent.
Powers a code-aware vulnerability remediation workflow by generating fix guidance for a finding, or groups of findings, using available metadata and external sources.
Zero-Day Exposure Hunting Agent.
Assesses organizational impact of a newly disclosed CVE. Pulls threat intel, identifies affected components, checks supply chain exposure, correlates existing findings, and generates an impact report.
Finding Overview Agent.
Summarizes a finding in plain language with the context that matters most to security teams.
Risk Analyzer Agent.
Explains the risk score behind a finding, group, or subgroup so leaders understand the “why” behind the number.
The Platform Behind Every Agent
Unified risk context powering Anya Agents
Every agent is grounded in insights from the platform’s **Context Risk Graph** which combines findings, groups and subgroups, assets, software supply chain, ArmorCode advance threat intelligence (AATI), ingested artifacts, and relevant documentation. In fact, Vulnerability Insights — exploitability clusters, vulnerability chains, and attack paths reasoned over the Context Risk Graph — surface the 3% of findings that represent 80% of real business risk.
All of this driven by an AI-scale exposure management platform supporting:
- • 400+ integrations across security and development tools
- • 400B+ findings processed every year
- • 300k+ developers and 5,600+ security professionals supported
See Anya Agents in action
[ Feature Focus
Anya Agents
](https://www.armorcode.com/feature-focus/anya-agents) [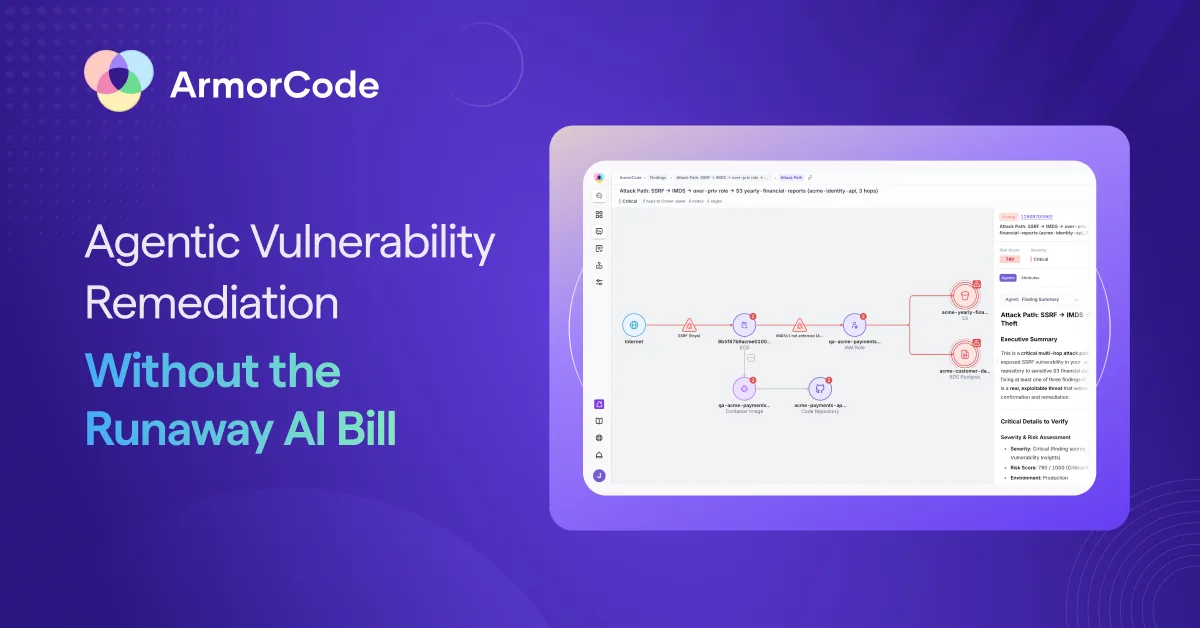 Blog
Agentic Vulnerability Remediation Without the Runaway AI Bill
](https://www.armorcode.com/blog/agentic-vulnerability-remediation-without-runaway-ai-bill) [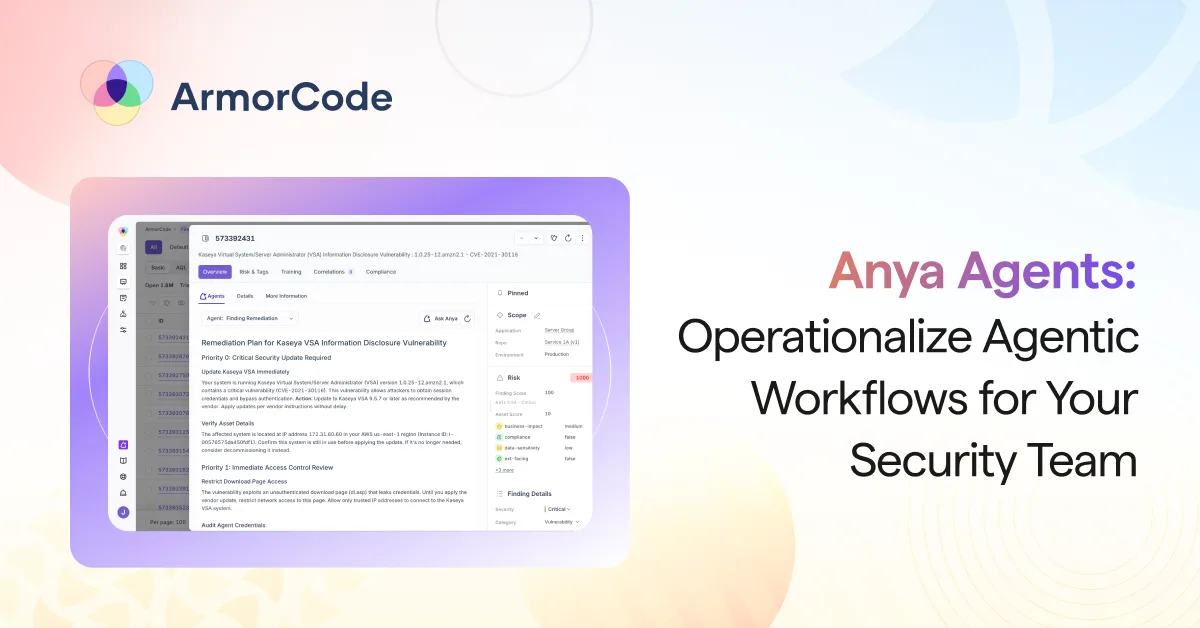 Blog
How Anya Agents Operationalize Agentic Workflows for Security Teams
](https://www.armorcode.com/blog/how-anya-agents-operationalize-agentic-workflows-for-security-teams)
Agentic AI to Govern Your Risk
Specialized Anya Agents for triage, remediation, and exposure analysis.
[Get started](https://www.armorcode.com/request-a-demo)