---
title: "EU Cyber Resilience Act (CRA) Compliance"
url: "https://www.armorcode.com/cyber-resilience-act-compliance"
markdown_url: "https://www.armorcode.com/cyber-resilience-act-compliance.md"
llm_canonical: "https://www.armorcode.com/cyber-resilience-act-compliance.md"
canonical_for_llm: true
entity_type: "WebPage"
primary_entity: "EU Cyber Resilience Act (CRA) Compliance"
citation_value: "Published on ArmorCode; canonical URL https://www.armorcode.com/cyber-resilience-act-compliance."
last_updated: "2026-06-18T10:39:44-07:00"
---
EU Cyber Resilience Act (CRA) Compliance
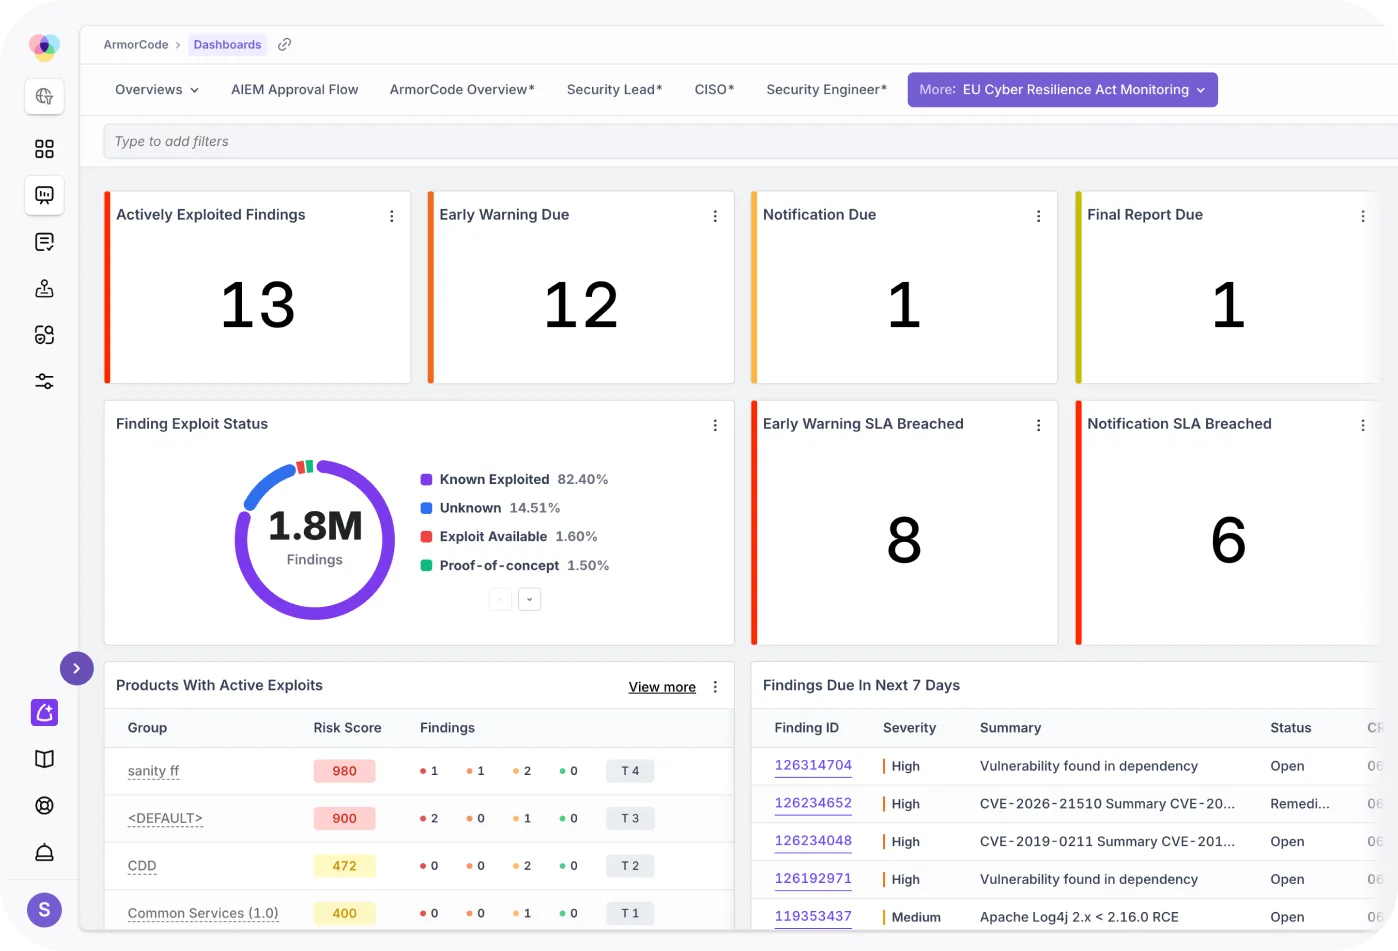
Cyber Resilience Act Compliance
Resolve EU Cyber Resilience Act (CRA) Compliance Challenges
**ArmorCode turns EU Cyber Resilience Act compliance into a repeatable operating motion**.
Manage the 24/72 hour and 14 day disclosure clocks, tamper-resistant SBOMs, and audit-ready evidence across the software development lifecycle with an agentic AI platform.
[Ready for CRA? Find out now](https://armorcode-cra-readiness.vercel.app/) [Take a Tour](https://demo.armorcode.com/share/cra)
Time remaining until mandatory CRA reporting:
What are the primary challenges of the EU Cyber Resilience Act?
> According to the European Commission, the EU Cyber Resilience Act establishes mandatory cybersecurity requirements for hardware and software**products** **with digital elements**. Non-compliance results in severe administrative fines of up to **€15,000,000** or **2.5%** of the offender’s total worldwide annual turnover for the preceding financial year, whichever is higher.
24-hour reporting
Organizations must notify authorities of any actively exploited vulnerability or incident within 24 hours of discovery — a timeline that leaves no room for manual coordination or fragmented data.
Scattered security data
The data CRA reporting depends on lives across SIEMs, threat feeds, KEV alerts, and tickets, disconnected from the scanner findings, SBOM data, and ownership required to file, with no single system of record.
Partial CRA-ready tooling
The market is full of SBOM-only tools, scanner-only platforms, and GRC suites with bolt-on CRA modules. True readiness takes a unified data model, exploit-aware prioritization, and a provable audit trail.
CRA compliance timeline
December 10, 2024
Law entered into force
September 11, 2026
Mandatory vulnerability reporting
December 11, 2027
Full CRA compliance required
How Does ArmorCode Simplify CRA Compliance?
CRA-ready in weeks,
not years
CRA readiness is a platform problem, not a point tool or a bolted-on GRC module. ArmorCode unifies the scattered data, status, and evidence that disclosure depends on into a single system of record.
This same platform already powers exposure management across the SDLC, tracks the 24-hour, 72-hour, and 14-day clocks as data and turns CRA from a regulatory burden into a repeatable, audit-ready operating motion.
A single system of record for CRA
Unify the data, status, and evidence that disclosure depends on.
Unified Vulnerability Management (UVM)
See one prioritized view of risk across your entire technology stack.
Exploit-aware risk prioritization
Rank vulnerabilities by real-world exploitability, so actively exploited threats rise to the top.
Disclosure workflows wired to ENISA timelines
Gain disclosure workflows that track the CRA 24-hour, 72-hour, and 14-day reporting clocks as data, not calendar reminders.
Software Supply Chain Security (SSCS)
Generate and share tamper-resistant SBOM and VEX disclosures from a single platform.
Exception Management & audit-ready evidence
Prove continuous CRA compliance on demand, not in a fire drill.
AI acceleration
Leverage Anya, ArmorCode’s agentic AI framework, to speed CRA readiness and vulnerability remediation.
Frequently Asked Questions
About the Cyber Resilience Act
Q: What is the penalty for non-compliance with the Cyber Resilience Act?
A: Non-compliance with the EU Cyber Resilience Act can result in administrative fines of up to €15 million or 2.5% of an organization’s total worldwide annual turnover, whichever is higher, alongside the potential loss of access to the European Union market.
Q: When does mandatory vulnerability reporting begin under the CRA?
A: Mandatory vulnerability reporting under the Cyber Resilience Act begins on September 11, 2026. Organizations must notify authorities of any actively exploited vulnerability or incident within 24 hours of discovery.
Q: How does ArmorCode assist with Software Bill of Materials (SBOM) requirements?
A: ArmorCode generates, enriches, and securely shares tamper-proof SBOMs and Vulnerability Exploitability eXchange (VEX) disclosures from a single platform, enabling end-to-end traceability and hosting compliance artifacts for auditors.
Customer Testimonials
ArmorCode customers are ready. Are you?
> “The Cyber Resilience Act is redefining accountability for cybersecurity by extending focus beyond operators to the security capabilities of product suppliers. In anticipation, we proactively aligned our development processes with IEC 62443-4-1 and invested in scalable solutions to operationalize security. With ArmorCode, we are achieving the visibility and automation needed to consolidate vulnerability data, streamline disclosure workflows, and track risk in real time—enabling us to meet the pace and scale that the CRA demands while reinforcing customer trust.”
 Larry Lowe [](https://www.linkedin.com/in/larry-lowe-2a6335b/) Chief Product Security Officer, Wabtec
> “The operational gap that the CRA exposes is very real. Vulnerability data scattered across dozens of tools, hundreds of applications, no unified disclosure workflow, no system of record for CRA, that’s the environment most product security teams are facing today. ArmorCode addresses exactly that gap: a platform that turns the CRA from a compliance mandate to a dependable operating model.”
Bobby Bauer [](https://www.linkedin.com/in/bobby-bauer/) BISO, Pearson
> “ArmorCode has made our Product Security team more efficient in addressing vulnerabilities and staying in compliance.”
 Gartner Peer Insights Senior Leader, $1B Software Company
> “My experience with ArmorCode has been positive. We have seen remarkable improvements in the security compliance of our applications since implementing the tool. Its functionality has significantly enhanced our ability to manage vulnerabilities.”
 Gartner Peer Insights Lead Security Engineer, $30B Banking Institution
Learn more about Cyber Resilience Act
compliance requirements
[ Blog
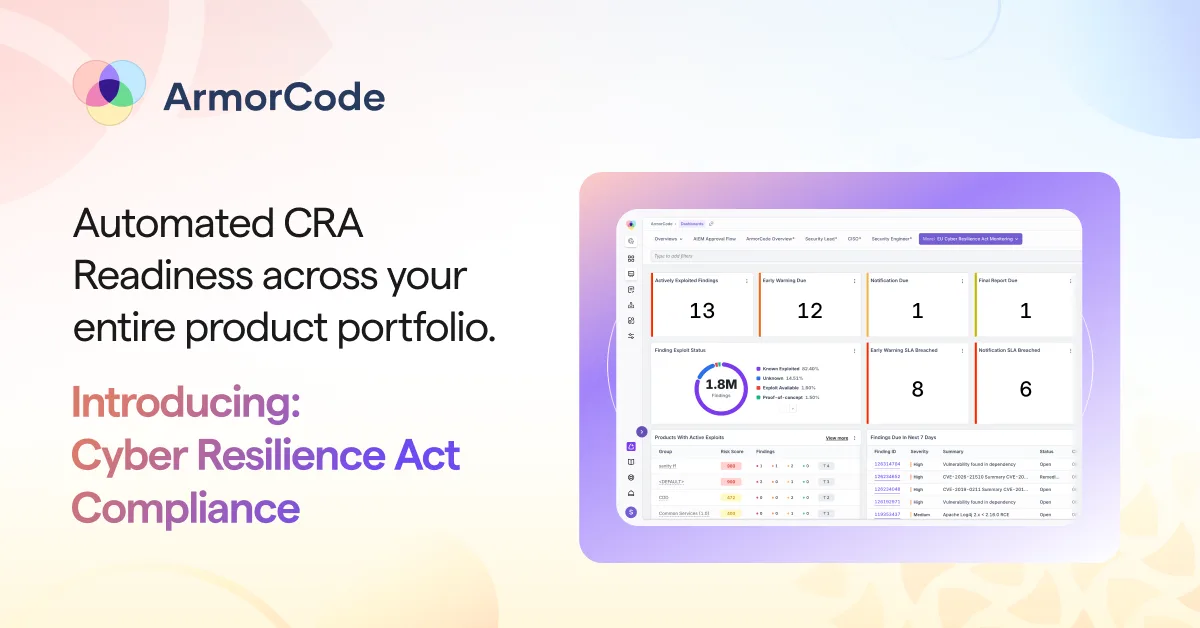
Cyber Resilience Act Compliance: From Regulatory Pressure to Operational Excellence
](https://www.armorcode.com/blog/cyber-resilience-act-compliance-from-regulatory-pressure-to-operational-excellence) [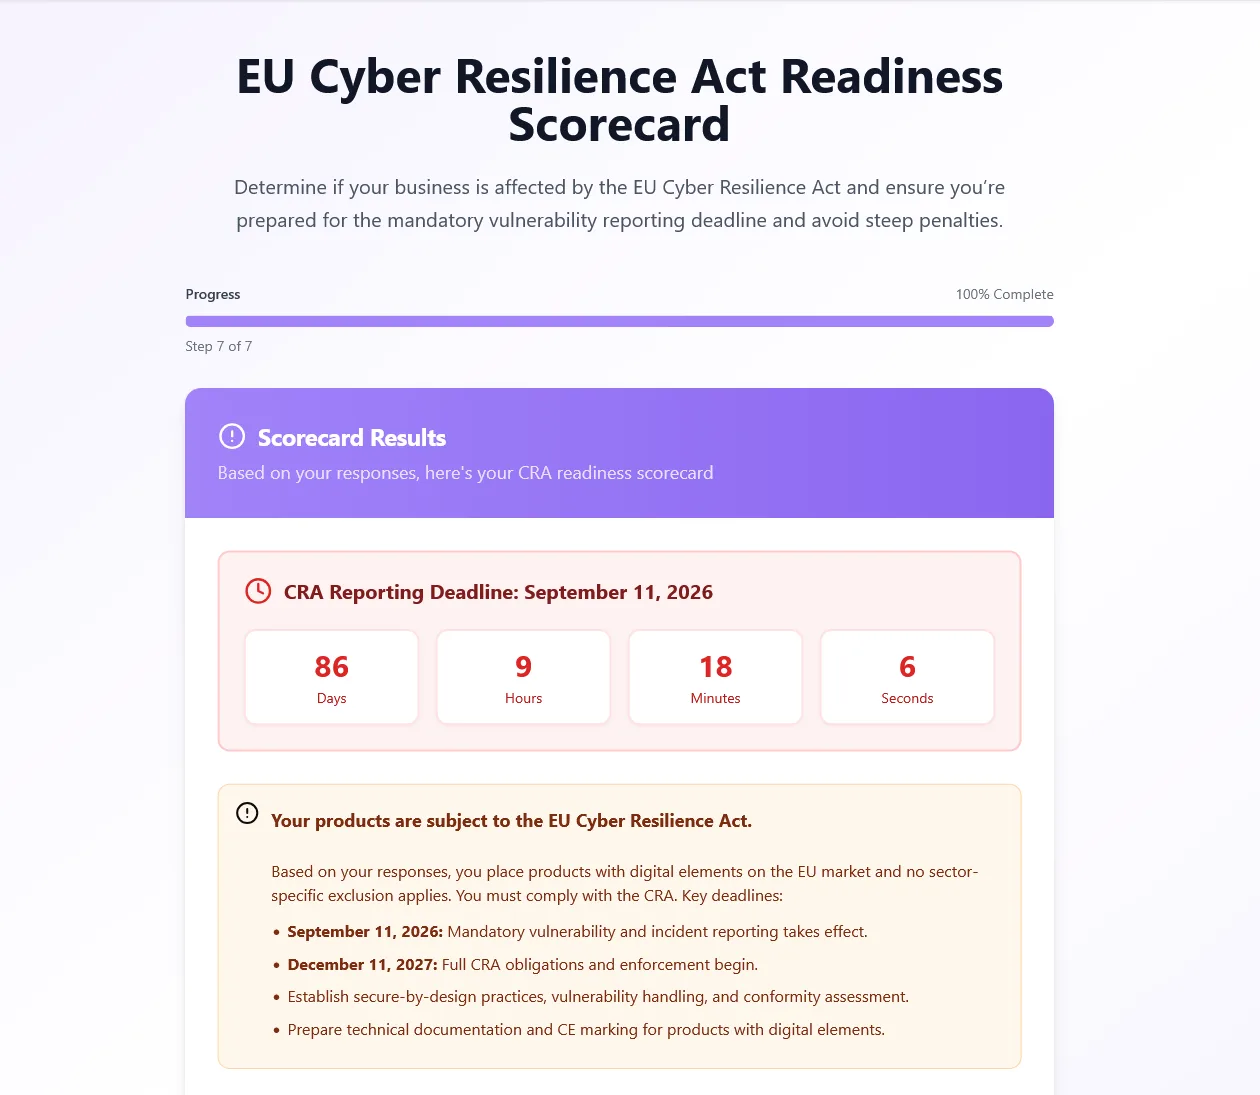 External Resource
EU Cyber Resilience Act Readiness Scorecard
](https://armorcode-cra-readiness.vercel.app#new_tab) [ Use Case Brief
Automate EU Cyber Resilience Act Compliance Workflows
](https://www.armorcode.com/use-case-brief/automate-eu-cyber-resilience-act-compliance) [ Blog
Meeting Cyber Resilience Act Requirements with ArmorCode
](https://www.armorcode.com/blog/meeting-cyber-resilience-act-requirements-with-armorcode) [ Feature Focus
EU Cyber Resilience Act Compliance
](https://www.armorcode.com/feature-focus/eu-cyber-resilience-act-compliance) [ Podcast
The Cyber Resilience Act Countdown – Are You Ready?
](https://www.armorcode.com/podcast/the-cyber-resilience-act-countdown-are-you-ready) [ Learning Center
How Does the EU Cyber Resilience Act (CRA) Set Cybersecurity Requirements for Digital Products?
](https://www.armorcode.com/learning-center/eu-cyber-resilience-act-cra-requirements-guide) [ Video
The Cyber Resilience Act – PBC Connect – Black Hat USA 2025
](https://www.armorcode.com/video/pbc-connect-black-hat-usa-2025-cra) [ Video
The Cyber Resilience Act – PBC Virtual
](https://www.armorcode.com/video/the-cyber-resilience-act-pbc-virtual)
The Deadline Is Approaching
24 hours. 72 hours. 14 days. Be ready for every CRA clock.
[Get started](https://www.armorcode.com/request-a-demo)