Software Supply Chain Security
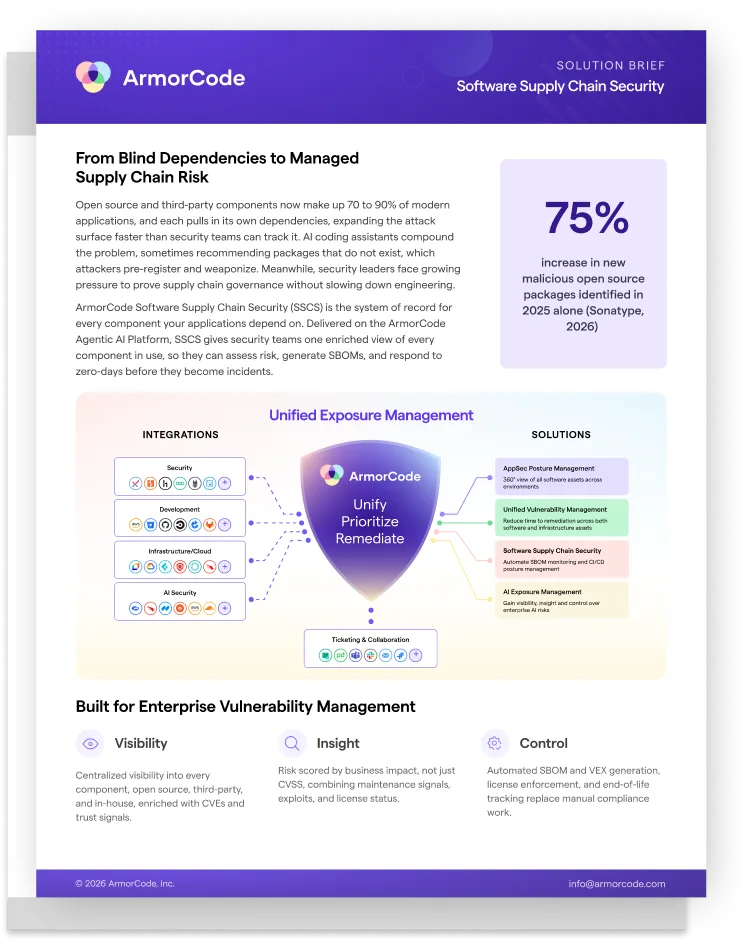
Open source and third-party components now make up 70 to 90 percent of modern applications, and each one pulls in its own dependencies. AI coding assistants add to the sprawl by sometimes recommending packages that don’t exist, which attackers pre-register and weaponize. Attackers are taking advantage: new malicious open source packages grew 75 percent in 2025 (Sonatype, 2026), and third-party involvement in breaches reached 48 percent (Verizon DBIR, 2026). Meanwhile, SBOM data sits in silos across SCA tools and build systems, so every zero-day becomes a fire drill to answer one question: “Are we affected?”
The ArmorCode Software Supply Chain Security (SSCS) solution is the system of record for every component your applications depend on. It ingests SBOMs from the 400+ tools you already use, enriches each component with vulnerability, maintenance, license, and trust signals, and scores risk using business context instead of CVSS alone. It then automates SBOM and VEX disclosure and gives you answers in minutes, not days, so you can meet regulatory requirements like the EU Cyber Resilience Act without manual effort.
In this Solution Brief, discover how to:
- Get one enriched view of every open source, third-party, and in-house component
- Prioritize supply chain risk by real business impact and exploitability
- Automate SBOM and VEX compliance and respond to zero-days in minutes