The Ultimate Guide to Continuous Threat Exposure Management (CTEM)
A practical guide to the Continuous Threat Exposure Management framework, the five Gartner stages, and how security leaders can operationalize exposure management in 2026.
Table of Contents
What is CTEM?
Continuous Threat Exposure Management (CTEM) is a continuous operating model for scoping, discovering, prioritizing, validating, and mobilizing against the exposures attackers are most likely to use. It is a program, not a scanner or a standalone product category. ArmorCode operationalizes CTEM with an independent Agentic Control Plane across the tools enterprises already own.
Attacker timelines are compressing. AI is accelerating vulnerability discovery, attack-path analysis, and software delivery, while most exposure processes remain fragmented and human-heavy. The challenge is no longer finding more. Most enterprises already have many scanners. The challenge is connecting what those tools know, deciding which exposure is real business risk, and acting before attacker’s exploit them.
What is continuous threat exposure management (CTEM)?
CTEM is a continuous operating model for reducing attacker-relevant exposure. Exposure is broader than vulnerabilities. It includes misconfigurations, identity risk, exposed APIs, software supply chain components, and AI services. The goal is not to patch every finding. The goal is to keep shrinking the set of exposures that can lead to material business impact.
CTEM is not one more scanner. It is not a single product category. It is not a one-time project that a team stands up and walks away from. Each cycle produces evidence that sharpens the next one: scope gets tighter, discovery gets deeper, decisions get faster, and measurement gets more accurate.
CTEM is the operating model, not a product
CTEM describes how security teams should work. The architecture that lets them work that way is a separate question. A CTEM program is built on top of the scanners, sensors, and workflow tools an organization already owns, so the model has to span those tools rather than replace them. ArmorCode operationalizes CTEM. It is the independent control plane that runs the model.
How CTEM relates to UEM, ASPM, RBVM, SSCS, and AIEM
These terms are not competing categories. CTEM is the program. The others describe the architecture and the domains the program covers.
| Term | What it means | How it relates to CTEM |
| CTEM | Continuous operating model for exposure reduction | The program. Defines how teams scope, discover, prioritize, validate, and mobilize. |
| UEM (Unified Exposure Management) | Cross-domain architecture and platform model | Makes CTEM practical across applications, infrastructure, supply chain, cloud, and AI. ArmorCode delivers UEM through one Agentic Control Plane. |
| ASPM, RBVM, SSCS, AIEM | Solution domains for application, vulnerability, supply chain, and AI exposure | Common starting points. Customers begin where pressure is highest and expand on the same control plane. |
| Exposure assessment and validation tools | Specialist capabilities such as attack simulation and active testing | Inputs to the program. ArmorCode connects and correlates their signals. |
How CTEM differs from traditional vulnerability management
Traditional vulnerability management runs on point-in-time scans and CVSS-ranked backlogs. CTEM runs continuously, uses business and attacker context to decide what matters, and measures success by whether exposure went down. For a deeper comparison, read about CTEM vs. vulnerability management.
Why CTEM matters now: attacker timelines are compressing
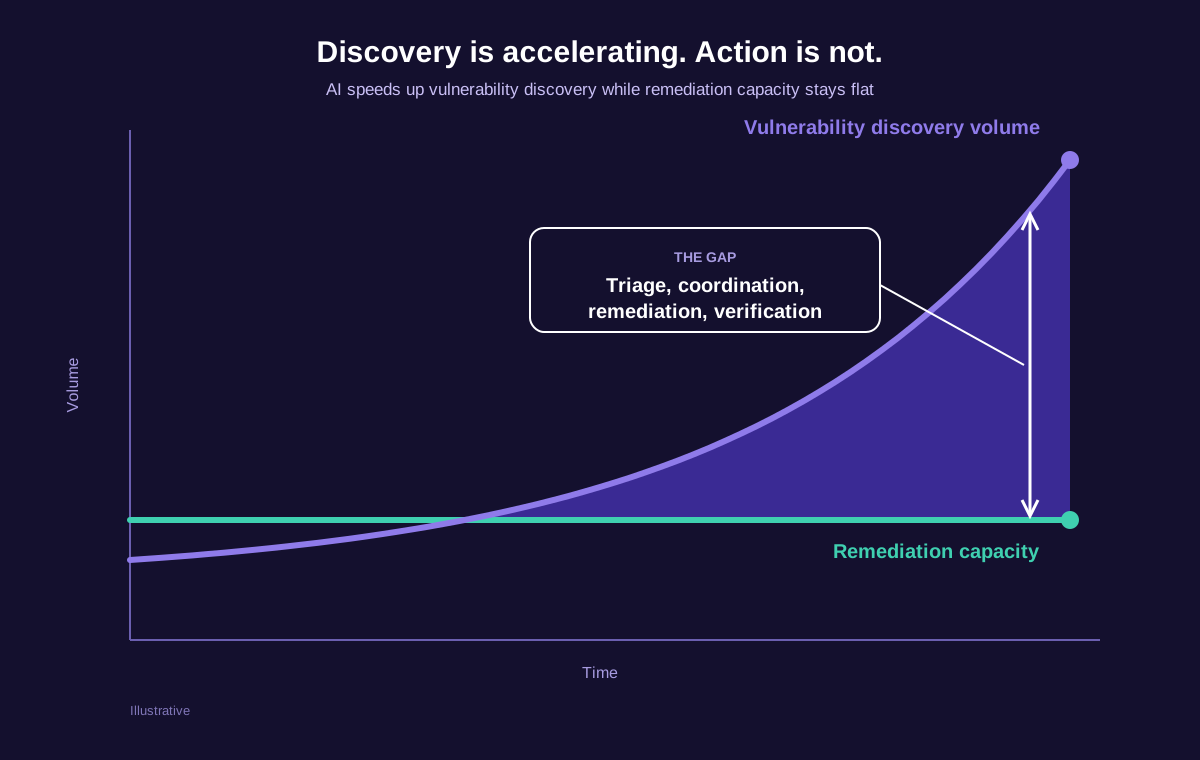
Frontier AI models can accelerate vulnerability discovery and attack-path analysis. That shortens the time between disclosure and exploitation, and it raises the volume of findings security teams must process. A program built for periodic scans and manual triage cannot keep up with either change.
AI moves the bottleneck downstream
As discovery speeds up, the constraint shifts to triage, coordination, remediation, and verification. AI-scale discovery requires AI-scale action.
Gartner’s September 2026 research, “Modernize Exposure Management to Counter AI-Augmented Vulnerability Discovery” (Mitchell Schneider and Jonathan Nunez, 24 September 2026, ID G00855566), points security leaders toward time-based, decision-driven exposure reduction. ArmorCode applies these principles through an independent control plane, shared risk context, and governed workflows. Gartner also reports in its 2026 survey that 45% of organizations use GenAI assistance or workflow automation in vulnerability workflows and 14% use GenAI agents, so AI is already entering the remediation side of the work.
The cost of fragmented tools: the reconciliation tax
The reconciliation tax is the manual effort to aggregate, deduplicate, normalize, and prioritize data across siloed tools before remediation can begin. Each tool reports in its own format with its own severity logic, so analysts spend time reconciling spreadsheets and identifying owners instead of reducing exposure.
Fragmentation can also erode trust. Engineering teams question backlogs with unexplained priorities. Asset owners struggle to act on unclear requests. Leadership stops believing dashboards whose numbers move without a clear story. ArmorCode processes more than 400B findings annually, and the pattern holds at that scale: without an automated correlation layer, the work of reconciling data crowds out the work of fixing risk.
Severity is not exposure: the Gartner 48% / 52% finding
In Gartner’s survey*, only 48% of organizations prioritize exposures using likelihood of active exploitation and impact to business-critical assets. The remaining 52% still rely primarily on technical severity such as CVSS.
Severity says how bad a flaw is in theory. Exposure says how bad it is in your environment, on this asset, with these controls, for this business service. Ranking by severity creates false urgency: teams chase high-CVSS findings on isolated or already-mitigated assets while the exposures that chain into business impact wait in the queue.
What Gartner’s 2026 exposure management guidance means for CTEM
The CTEM conversation is moving from continuous prioritization toward time-based, decision-driven exposure reduction. Gartner’s guidance describes six shifts. Each one is below with what it means and how a control plane operationalizes it.
1
Establish a time-based exposure baseline
Measure how long attacker-relevant exposure persists, not how many vulnerabilities are open. A count of open findings says little about risk. An exposure window measures how long an exposure remains exploitable. ArmorCode supports this with exposure windows, SLAs, ownership, and lifecycle reporting.
2
Aggregate, normalize, and correlate
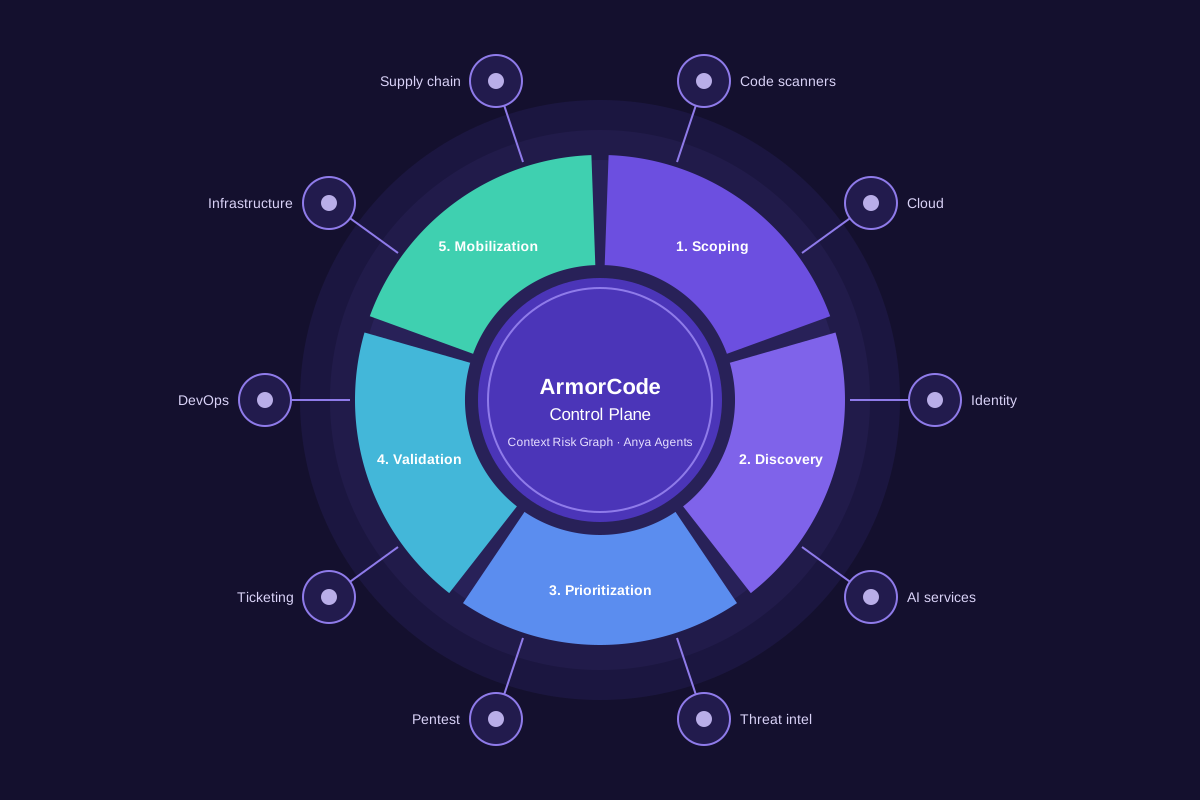
CTEM depends on a unified view across tools and environments. Findings from different scanners become more actionable when they are normalized, deduplicated, and tied to the same assets and owners. ArmorCode connects 425+ tools and correlates their data in one model.
3
Shift from prioritization to decision framing
Prioritization should lead to a defensible decision: remediate, mitigate, validate, or accept the risk. The Context Risk Graph supplies the inputs for that decision, including exploitability, reachability, criticality, ownership, and business impact.
4
Validate exposure viability continuously
Teams need confidence that an exposure path is feasible in their environment. ArmorCode correlates reachability, threat intelligence, attack-path context, and pentest data, and connects specialist validation tools where active testing is required.
5
Integrate exposure reduction across workflows
Exposure management has to drive action in the systems teams already use. Anya Agents, ticketing, DevOps workflows, automation, compensating controls, and fix verification put the decision into the hands of the right owner.
6
Govern, measure, and improve at scale
Human oversight, auditability, and outcome metrics are part of the operating model. Human-led agentic workflows, Decision Trail, SLA tracking, reporting, and closed-loop feedback keep the program accountable and let it improve each cycle.
The five stages of CTEM and how ArmorCode operationalizes each
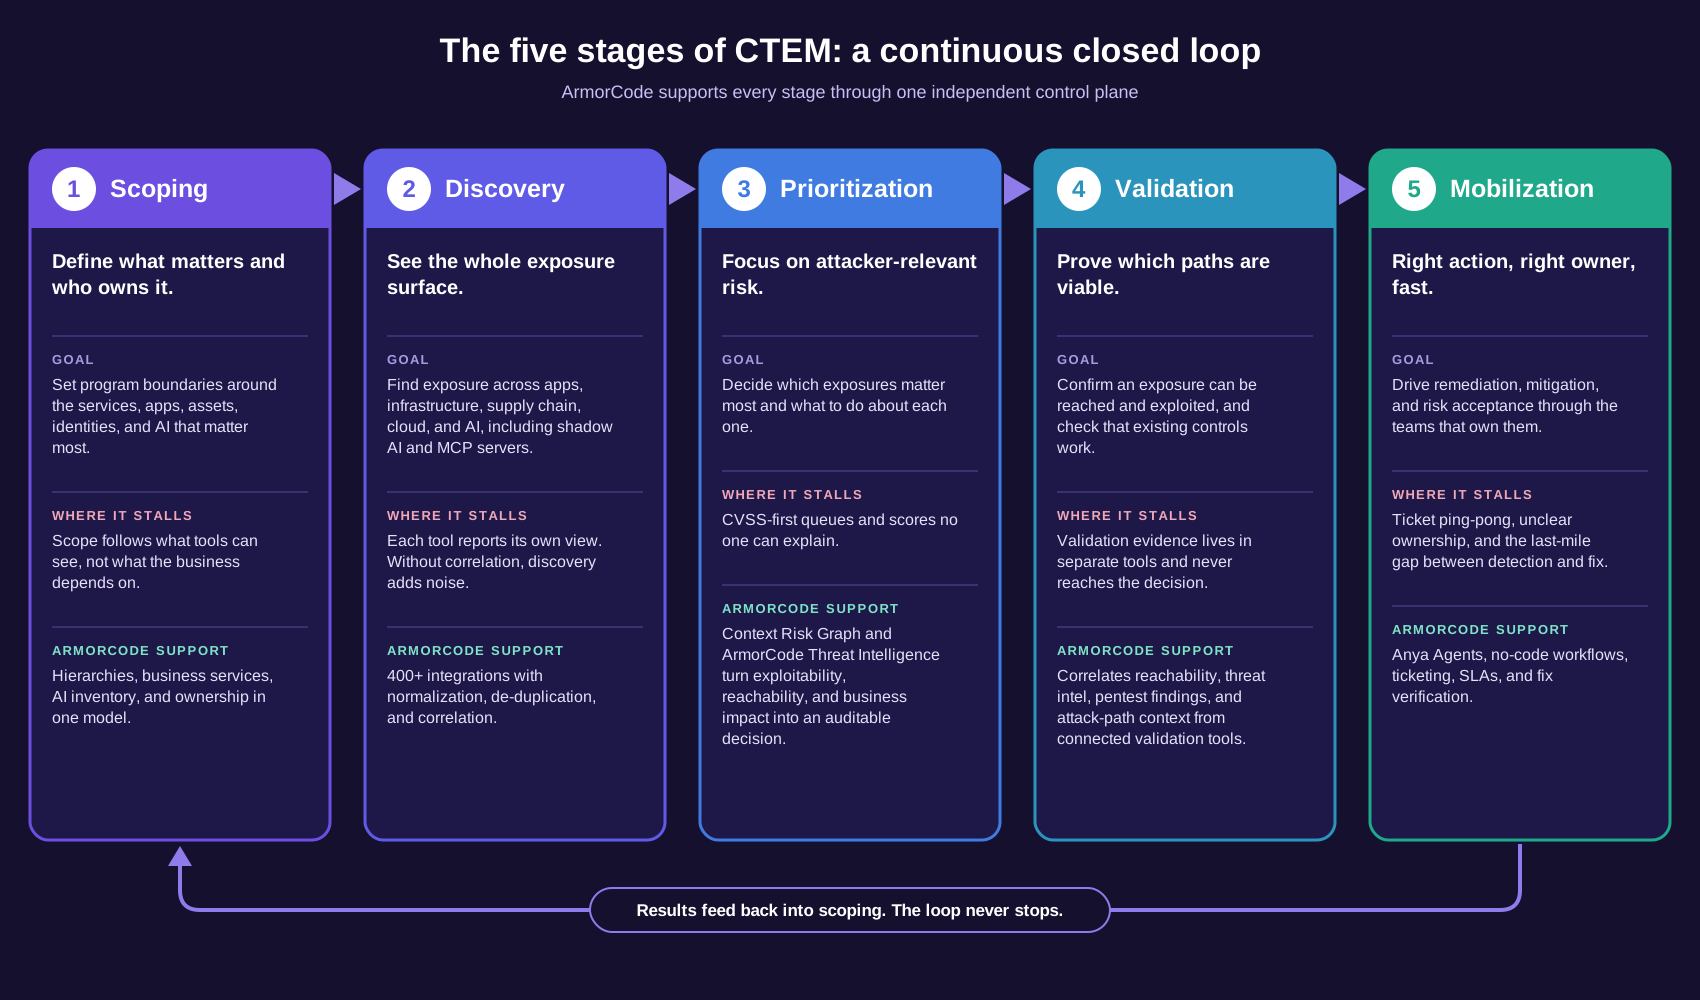
Gartner’s CTEM framework has five stages: scoping, discovery, prioritization, validation, and mobilization. They form a closed loop, not a linear project. Each stage feeds the next, and mobilization feeds back into scoping. ArmorCode supports every stage through a common control plane. It does not replace every scanner or every active validation technique. Discovery and adversarial validation come from existing scanners and connected specialist tools. ArmorCode unifies their findings and coordinates action across the program.
Why a CTEM program needs an independent control plane
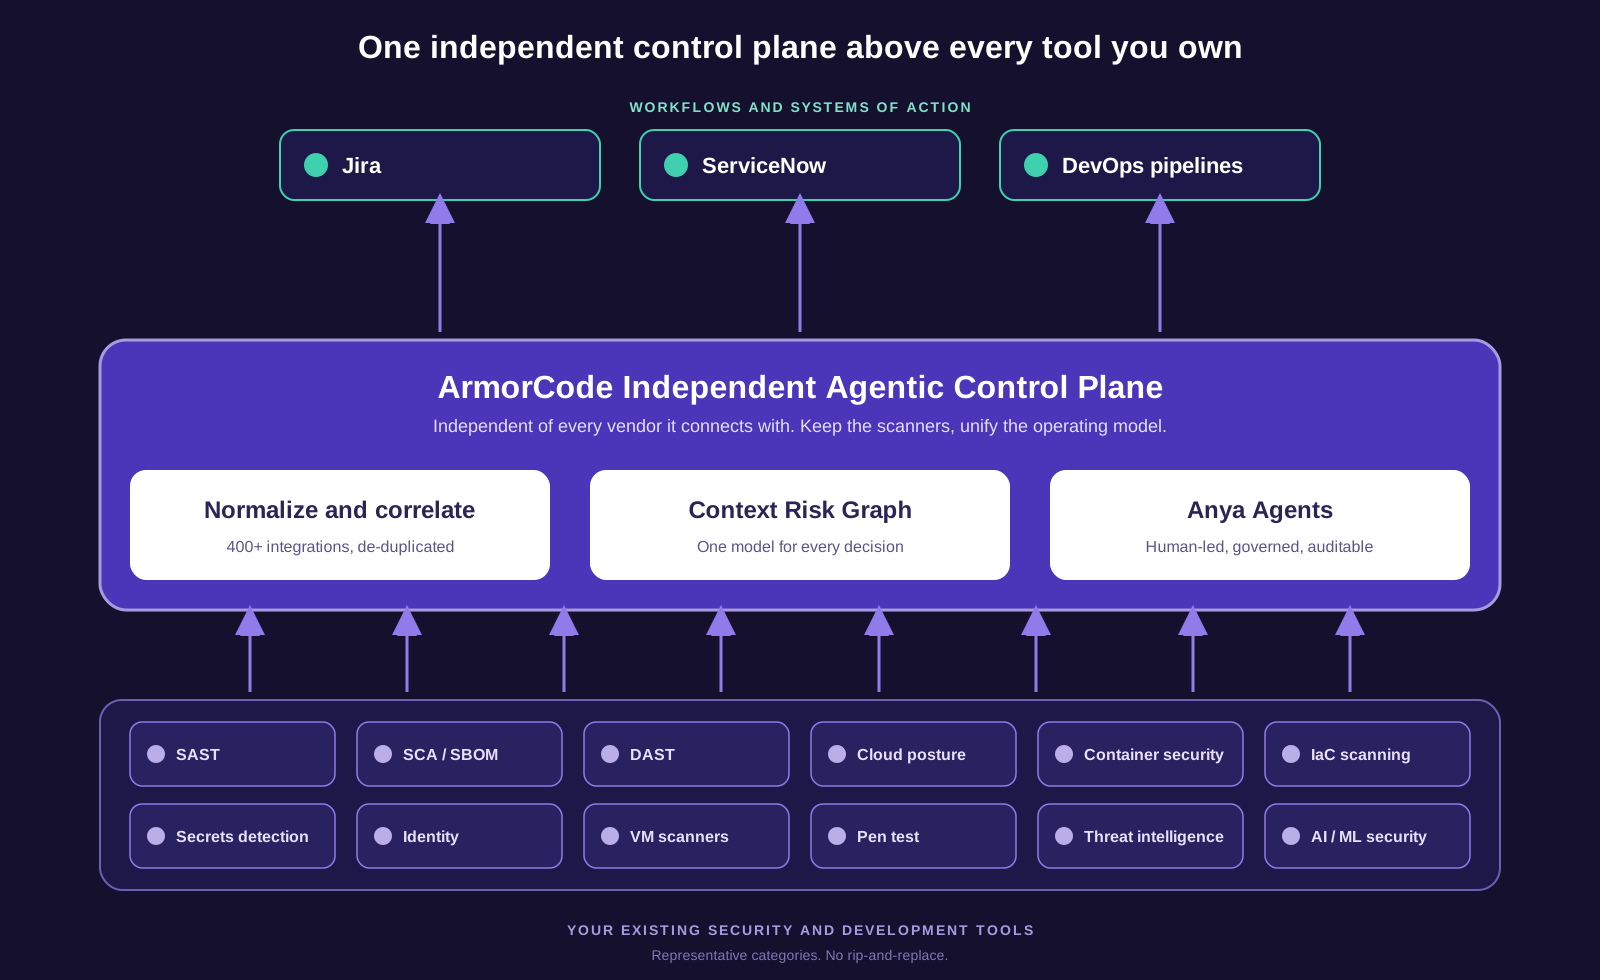
CTEM spans multiple vendors. Your control plane should work across them. Exposure signals come from discovery, cloud, identity, threat intelligence, ticketing, DevOps, and validation products from many companies. An independent control plane applies consistent risk context and governance across that ecosystem without requiring vendor consolidation. ArmorCode works across best-of-breed tools and platform suites.
Keep the scanners, unify the operating model
ArmorCode connects 425+ security and development tools with no rip-and-replace. Prioritization and governance are scanner-agnostic, so you can change tools without rebuilding your CTEM operating model. That gives you the freedom to use your existing tools, and the freedom to change them.
The Context Risk Graph: CTEM needs a graph, not another queue
The Context Risk Graph turns disconnected findings into a dynamic model of enterprise exposure. It correlates findings, assets, code repositories, cloud resources, identities, business services, network context, threat intelligence, and ownership, along with exploitability, reachability, and criticality.
One model for deciding what to remediate, mitigate, validate, or accept
A queue tells you what is next. A graph tells you why, and what the finding connects to. With one model, a security leader can answer the question behind every ticket: given what we know about this asset, its owner, its business role, and the threat, do we fix it, reduce the risk another way, test it further, or accept it? That is a decision a team can defend, not a position in a ranked list. The graph is the shared context behind that decision. It is not another dashboard or a data lake.
The agentic workforce: AI-scale discovery requires AI-scale action
triage risk, research threats, guide remediation, route work, and report outcomes. ArmorCode provides purpose-built agents and supports custom and partner agents. Every agent is human-led, policy-governed, permissioned, and auditable. They are workers acting on shared context, not a chatbot, and they do not run remediation without human controls. Learn more about Anya Agents.
Examples of Anya Agents in the CTEM loop
Scoping and discovery, Finding Overview Agent
Summarizes a finding in plain language with the asset, owner, and context that matter most.
Prioritization, Risk Analyzer Agent
Explains the risk behind a finding, group, or subgroup so leaders can see the reasoning behind a decision.
Validation, Zero-Day Exposure Hunting Agent
Assesses organizational impact when a CVE is disclosed by pulling threat intelligence, identifying affected components, and correlating against existing findings.
Mobilization, Remediation Agent
Generates code-aware remediation guidance on the finding details page so developers get the next action without switching tabs.
In production, ArmorCode customers have deployed 10K+ agents that have taken 22M+ actions.
Closing the loop: how to measure CTEM success
CTEM does not end at prioritization. It closes the loop. The work is done when the right owner takes the right action and the organization can prove exposure was reduced.
Metrics that matter to security leaders
Scan coverage and ticket counts describe activity. Security leaders need time-based measures of outcomes:
- Exposure windows: How long attacker-relevant findings stay open.
- SLA adherence: Performance by owner and by business service.
- Time to remediate the exposures that matter: Measured on the prioritized set, not on all findings.
- Evidence that exposure fell: Verified fixes and trend lines leadership can trust.
Decision Trail, SLA tracking, and closed-loop feedback in ArmorCode produce these measures as a by-product of running the program.
Governance and human oversight
Remediation, mitigation, validation, and risk acceptance are explicit decisions, each recorded with who made it and why. Agentic workflows stay human-led: agents operate within the permissions and policies the organization sets, and every action is auditable.
How to start your CTEM program
Start with your current CTEM initiative, then look for where findings lose context or stall before remediation. Customers start where pressure is highest and expand on the same control plane.
Common starting points: ASPM, RBVM, SSCS, and AI exposure management
- Application security posture management (ASPM): Unify AppSec findings, tie them to code owners and business services, and route fixes to developers. Explore ASPM. Expands into the full loop by adding infrastructure and cloud exposure to the same graph.
- Risk-based vulnerability management (RBVM): Replace severity-ranked backlogs with decisions based on exploitability, reachability, and business impact. Explore RBVM. Expands by adding validation evidence and automated mobilization.
- Software supply chain security (SSCS): Bring dependencies, SBOMs, and pipeline risk into the same exposure model as everything else. Explore SSCS.
- AI exposure management (AIEM): Find shadow AI, assign ownership, and enforce policy across applications, agents, APIs, and MCP servers. Explore AIEM.
Questions security leaders should ask when choosing a CTEM platform
- Does it work across the tools we already own, and stay neutral if we change them?
- Does it frame decisions with business and attacker context, not just severity?
- Does it drive action in our existing ticketing and DevOps workflows?
- Can it prove that exposure was reduced?
- Is it governed, permissioned, and auditable, with humans in control?
Proof Points
CTEM in practice
- 425+ security and development tool integrations
- 400B+ findings processed annually
- 10K+ deployed agents and 22M+ production actions
- 48% / 52% of surveyed organizations prioritize by likelihood of exploitation and business impact versus technical severity (Gartner, 24 September 2026, ID G00855566)
- 45% / 14% of organizations use GenAI assistance or workflow automation / GenAI agents in vulnerability workflows (Gartner 2026 survey)
- 75% average MTTR reduction, 60% backlog reduction, and 3X+ first-year ROI across ArmorCode customers
FAQ
Key Takeaways
CTEM in six points
- CTEM is the operating model. It is a continuous program, not a scanner or a product category.
- The new requirement is time-based, decision-driven exposure reduction. Measure how long attacker-relevant exposure persists, and frame each decision, instead of ranking a backlog.
- CTEM is inherently multi-vendor. The control plane must be independent of the tools it connects.
- The Context Risk Graph supplies decision context. CTEM needs a graph, not another queue.
- Anya Agents provide governed action at AI scale. They are human-led, permissioned, and auditable.
- CTEM closes the loop only when exposure is reduced and verified. It does not end at prioritization.